How do I test a webhook?
Create a test URL on this page, register it as the webhook endpoint in the provider's settings, and trigger an event. The request appears in the inspector a moment later with its method, headers and body. No provider handy? Run the curl command shown under the URL or press Send test request.
Is the webhook tester free?
Yes, and it needs no account. Press the button, get a URL, send requests to it. There is nothing to install and nothing to pay for.
How long does my test URL live?
30 minutes. After that the URL stops accepting requests and everything it captured is gone. Create a new one whenever you need it.
Where are the captured requests stored?
In memory on our server in the EU, for the lifetime of the URL only. They are never written to a database or disk, and when the URL expires they are gone for good.
Can someone else read my captured requests?
Not from the URL alone. The URL you give a provider can only send requests; reading them needs a separate token that stays in your browser tab. Treat the tester as a scratchpad all the same: send test payloads, not production secrets.
How is this different from webhook.site or RequestBin?
It does the same basic job: a throwaway URL that shows you every request sent to it. The differences are that it runs on a server in the EU, keeps requests in memory only, deletes them after 30 minutes, and checks Stripe, GitHub, Shopify and Slack signatures against your secret in the browser. There is no paid tier to push you toward. If you need a URL that lives longer or replies with a custom status, use the self-hosted version below.
Is there a self-hosted version?
Yes. Webhook Tester is our open-source request bin that runs in one Docker container on your own server. It keeps requests in SQLite and can reply with any status code, which the online tester cannot. Use it when payloads carry customer data or when you want to watch a provider retry.
Can I test a webhook handler running on localhost?
The online tester only receives, so it cannot call your laptop. To send signed Stripe, GitHub or Shopify events to a handler on localhost, use Webhook Mock Sender, our open-source CLI. To forward real provider webhooks to localhost, use the Webhooker CLI, whk. To see what a real provider sends first, catch one request here.
Can it forward requests to my app?
No, the tester only receives. Forwarding, retries, signature checks on every event and replay are what a Webhooker source does, and the free plan covers 10,000 events a month.
Is my signing secret sent to Webhooker?
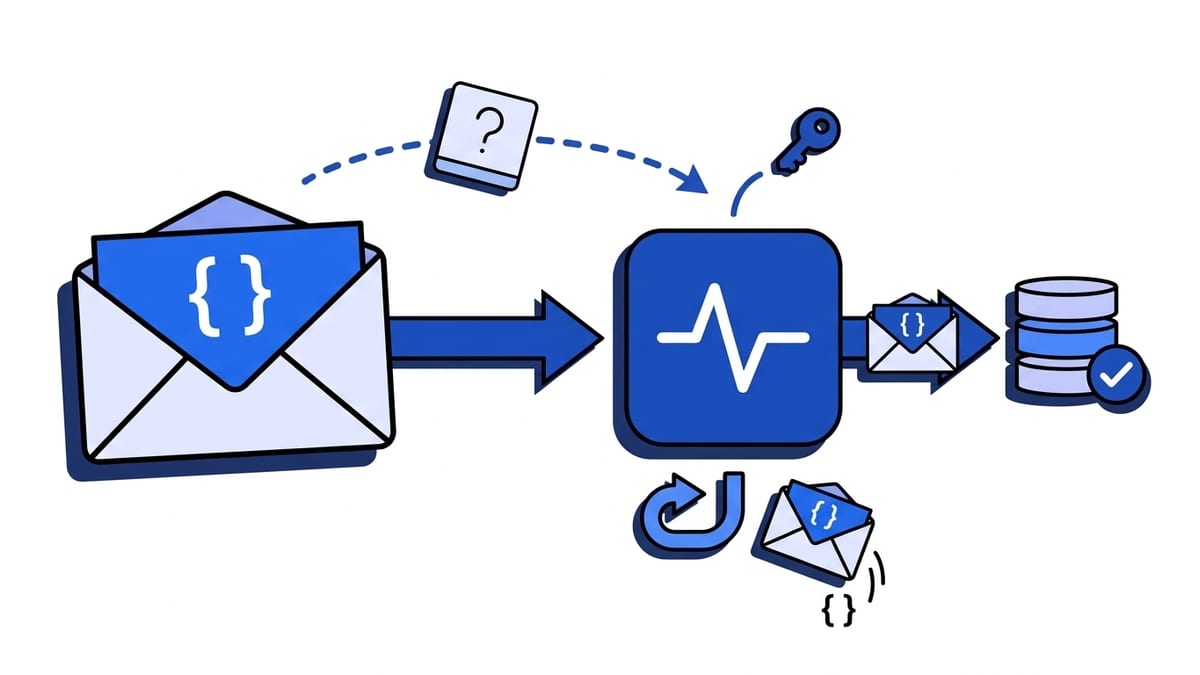
No. The secret stays in your browser tab. The page computes the HMAC with the Web Crypto API and compares it with the signature header there. The secret is not stored, not written to session storage and not sent to our servers or to analytics. Reload the page and it is gone.
Why does my Stripe signature fail when the secret is right?
Almost always because the body changed before it was hashed. Stripe signs the exact bytes it sent, so a framework that parses the JSON and serialises it again (express.json() is the usual one) produces a different string. The other common cause is a secret from another endpoint: the Stripe CLI, each Workbench destination and test and live mode all have their own whsec_ value. If the tester says valid and your code says invalid, your code is hashing something else.
Can I verify Shopify webhooks with the API key?
No. Shopify signs webhooks with the app's client secret (API secret key), not the API key, and the X-Shopify-Hmac-Sha256 header is base64, not hex. Store webhooks created in the admin use the secret shown under Settings, Notifications, Webhooks.
What is the size limit for a request?
128 KB per request, and the body is kept and shown byte for byte. A URL keeps up to 20 recent requests or 256 KB in total, whichever comes first, and drops the oldest as new ones arrive.
 Webhooker